TeamSync
Why TeamSync
Intelligent-repositoryDocuTalkeSignaturesAudit TrailContract Lifecycle ManagementSecurity & DeploymenteDiscoverySemantic SearchAI SummarisationMetadata Extraction + OCR/ICRRBAC + Backup + RestoreAgentic AI WorkflowView all capabilities →
Finance & BankingHealthcareEnergy & UtilitiesManufacturingPublic SectorAEC
Compliance
BlogsFAQsCase StudiesWhite PapersBecome a Partner
Contact
Intelligent-repositoryThe platformDocuTalkAI on your corpus eSignaturesSES, AdES, QESAudit TrailWorkflow & auditContract Lifecycle ManagementNative, not bolted-onSecurity & DeploymentDeploy your wayeDiscoveryHold at the sourceSemantic SearchHybrid retrievalAI SummarisationCitation-groundedMetadata Extraction + OCR/ICRCapture, typedRBAC + Backup + RestoreThe control surfaceAgentic AI WorkflowAI that acts
View all capabilities
Finance & BankingPCI, SOX & AML-ready document workflows for banksHealthcareHIPAA-first records, clinical workflows, audit trailsEnergy & UtilitiesPermits, safety & environmental compliance at scaleManufacturingCompliance-ready document workflowsPublic SectorFOIA, FedRAMP & records management for agenciesAECRFI, submittal & closeout document control at scale
View all industries
BlogsPractical writing on regulated content and AIFAQsCommon questions on deployment, security & complianceCase StudiesMeasured outcomes from regulated deploymentsWhite PapersTechnical papers on architecture, audit & regulationBecome a PartnerJoin our partner ecosystem and grow with TeamSync
TeamSync

The regulated content + AI platform for financial services, healthcare and life sciences, public sector, legal, energy, and AEC.

Capabilities
  • All Capabilities
  • DocuTalk AI
  • Electronic Signatures
  • Intelligent Repository
  • Audit Trail
  • E-Discovery
  • Contract Management
Industries
  • Financial Services
  • Healthcare
  • Energy
  • Manufacturing
  • Public Sector
  • AEC
Compliance
  • All Compliance
  • DPDP
  • HIPAA
  • SOC 2
  • ISO 27001
  • FedRAMP High
  • GDPR Art. 17
  • eIDAS QES
  • FDA 21 CFR Pt. 11
Resources
  • All Resources
  • Blog
  • FAQs
  • Case Studies
  • White Papers
  • Honest comparison
AboutTermsPrivacyDPASub-processorsCookie PolicySitemap
© 2026 TeamSync. All rights reserved.TeamSync is a product of AngelBot AI.
Follow us

Compliance Reporting on a Tamper-Evident Audit Trail

Regulated businesses spend weeks preparing for every audit. TeamSync eliminates that scramble entirely. Compliance reporting stays always-on and always complete. Every action, signature, edit, or approval, gets an immutable, blockchain-anchored timestamp. Auditors get independently verifiable proof, not a log file someone with admin access could alter.

Read more
  • EveryDocument event captured in an immutable audit trail
  • 100%Complete visibility into user and document activity
  • Tamper-EvidentRecords built for regulatory compliance
[Image: Audit trail dashboard with Merkle hash chain visualization and timestamped events]
  • EveryDocument event captured in an immutable audit trail
  • 100%Complete visibility into user and document activity
  • Tamper-EvidentRecords built for regulatory compliance
Scroll

Drive enterprise transformation with
Compliance & Audit Trail

Capture every change, approval, and access event in a single audit trail.

Blockchain-Backed Timestamps

Every signature, edit, and approval gets an immutable, blockchain-anchored timestamp, proof of exactly when it happened, not a database log someone with admin rights could alter. Auditors can verify it independently, without trusting your IT team.
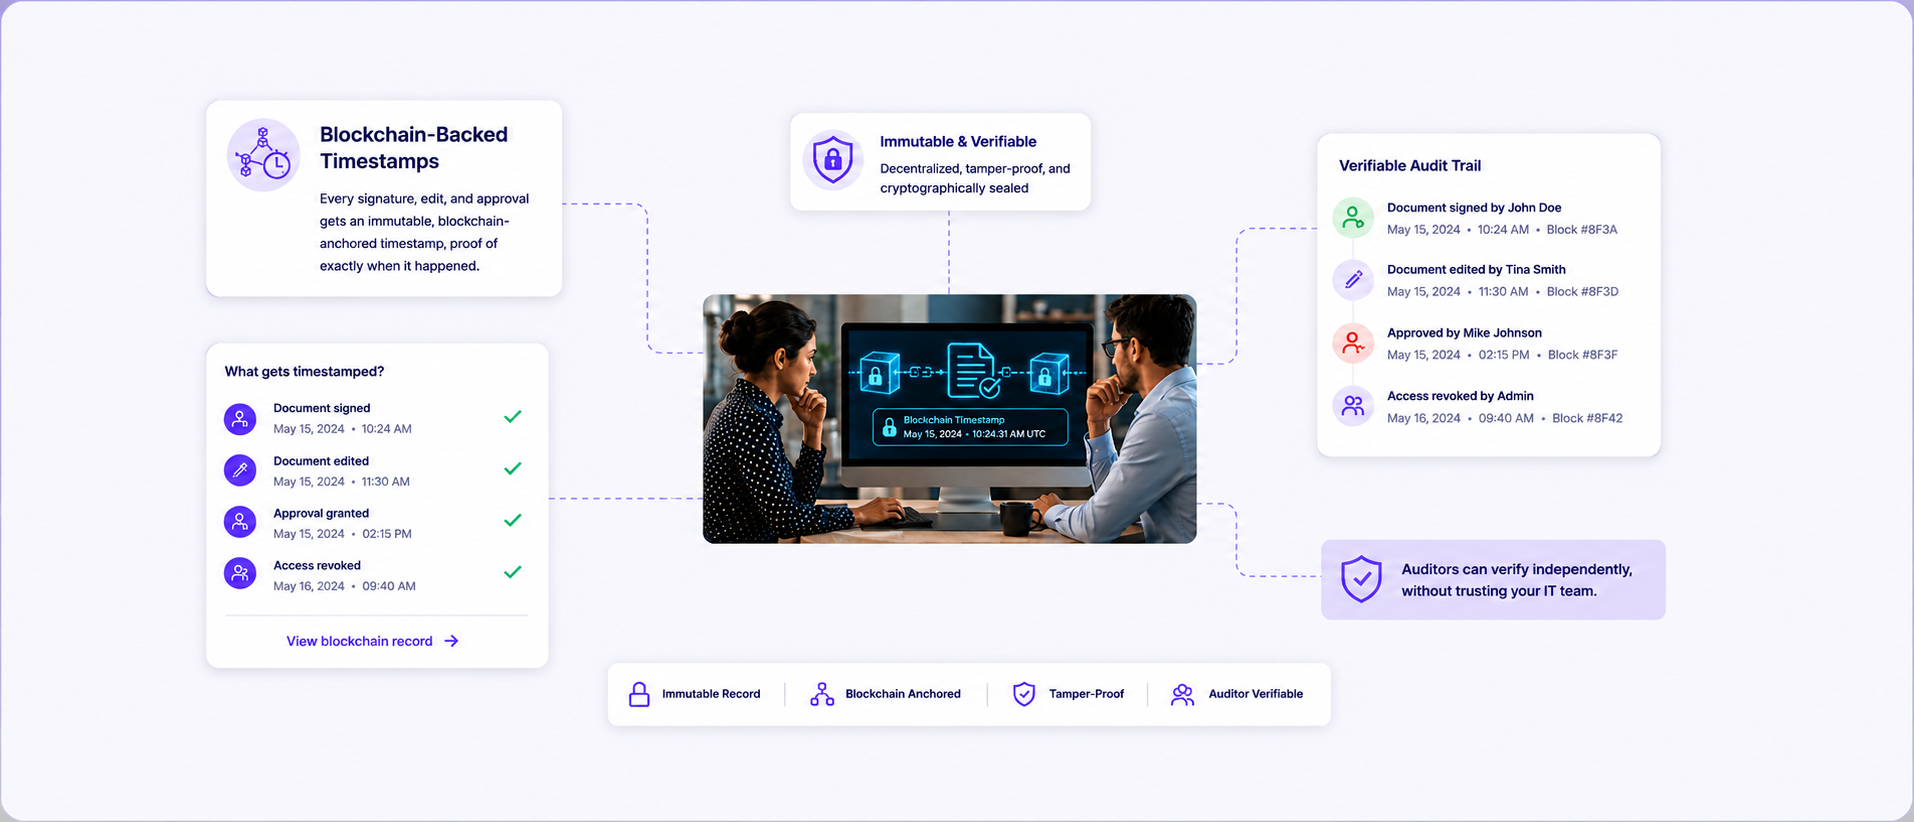
Blockchain-Backed Timestamps

What Your Team Actually Gets

Weeks to minutes

Audit preparation that used to take weeks now takes minutes with automated, always-current export packages.

01

Cryptographic proof

Merkle tree blockchain anchoring with external timestamping gives you mathematical proof of record integrity, not just log entries.

02

Multi-regulation support

SOC 2, HIPAA, GDPR, FINRA, FDA, FedRAMP, and SOC 2 AI controls are all configurable from one interface.

03

How Enterprises Use TeamSync Every Day
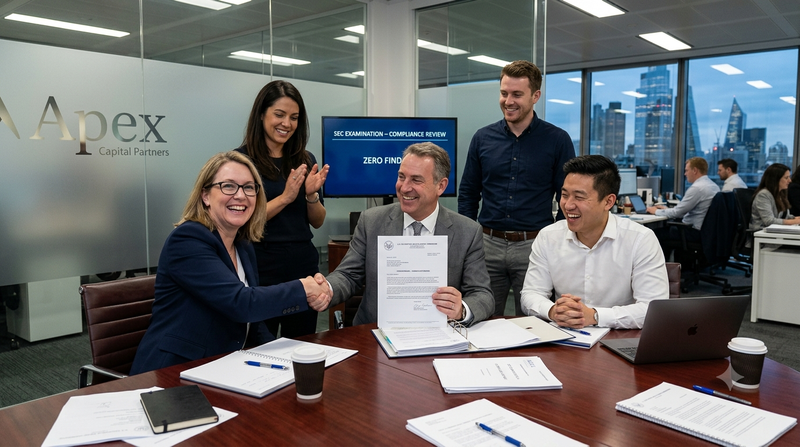
Investment firm passes SEC examination with zero findings
Financial Services

Investment firm passes SEC examination with zero findings

A top investment firm used TeamSync's automated version and export packages to produce the documentation required for examination in hours instead of weeks.
0
Examination findings
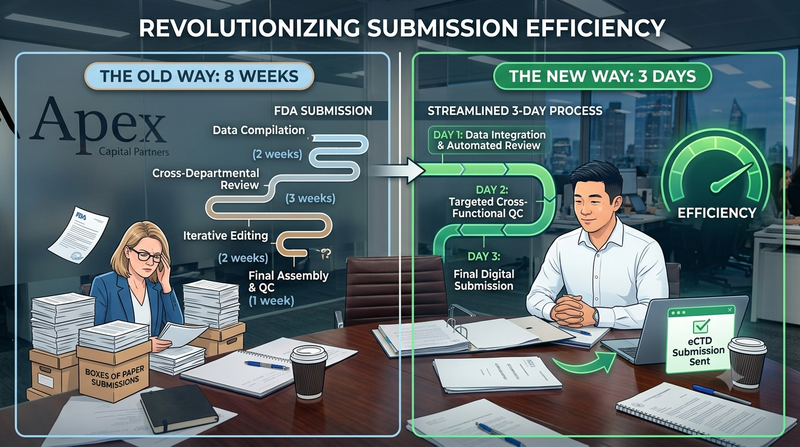
Pharma company cuts FDA submission prep from 8 weeks to 3 days
Life Sciences

Pharma company cuts FDA submission prep from 8 weeks to 3 days

Automated compliance packaging and tamper-evident trail eliminated manual document assembly across clinical trial records.
3 days
down from 8 weeks
Utility provider automates NERC CIP compliance documentation
Energy

Utility provider automates NERC CIP compliance documentation

Critical infrastructure compliance is now always-on with automated reporting configured from a single interface across all facilities.

24/7
Always-on reporting

Compliance & Audit FAQs.
Let's clear things up.

We know — retention schedules, audit evidence and regulator requests can feel overwhelming. TeamSync brings compliance into the platform itself.

Whether you are preparing for an audit or proving a record was never altered, we are here to make the evidence easy to produce.

  • It is the work of producing evidence that your controls operated as documented over a period. Where the evidence lives in an append-only ledger, that reporting becomes a filtered export rather than a manual reconstruction from several systems.

  • Actor, action, timestamp and context for every view, edit, download, permission change, workflow step and AI action, in a record that cannot be edited after the fact. If any of those are missing, the auditor has to take a system's word for it.

  • Not on its own - anyone with administrative rights can alter a database log. Entries here are cryptographically chained and anchored with blockchain-backed timestamps, so an alteration breaks the chain and an auditor can verify integrity independently.

  • It depends on the regime - FINRA 17a-4, FDA 21 CFR Part 11, HIPAA and SOX all set different periods. Retention schedules run automatically per regulation and document type, with legal-hold override, so multiple regimes can apply to the same estate.

  • Yes. Controls are mapped to SOC 2 Type II, ISO 27001, GDPR, HIPAA, PCI-DSS, GLBA, FINRA and NERC CIP from one interface, so one set of evidence answers several frameworks instead of being assembled separately for each.

View all FAQs
Talk to us

30 minutes with a solutions engineer who already speaks your industry.

No pitch deck. We will either show you a clear path forward or tell you we are not the right fit. Bring the toughest question on your desk this week.

Read more